Discovering Gamaredon’s Evolving Cyberespionage Tactics in 2024

02 Jul 2025
•
,
6 min. read

As the world grapples with the aftermath of Russia’s invasion of Ukraine, cyberespionage has emerged as a critical component of the ongoing conflict. ESET Research has been closely monitoring the activities of threat actors like Gamaredon, shedding light on their updated toolset and tactics observed throughout 2024.
Key takeaways from our analysis:
- Gamaredon intensified its focus on targeting Ukrainian governmental institutions in 2024, moving away from previous attempts against NATO countries.
- The group ramped up its spearphishing campaigns, utilizing new delivery methods such as malicious hyperlinks and LNK files executing PowerShell commands from Cloudflare domains.
- Introduction of six new malware tools by Gamaredon, leveraging PowerShell and VBScript for stealth, persistence, and lateral movement.
- Significant enhancements to existing tools, including improved obfuscation, stealth tactics, and advanced methods for lateral movement and data exfiltration.
- Gamaredon concealed its C&C infrastructure behind Cloudflare tunnels and increasingly relied on third-party services like Telegram, Telegraph, Cloudflare, Dropbox, and DNS-over-HTTPS for protection.
In a previous analysis titled “Cyberespionage the Gamaredon way: Analysis of toolset used to spy on Ukraine in 2022 and 2023,” we delved into Gamaredon’s aggressive activities against Ukrainian entities. Building on that research, we conducted a detailed examination of Gamaredon’s operations in 2024. For a deeper dive into our findings, check out our latest white paper.
Our investigation reveals that Gamaredon continues to pose a significant threat by adapting its strategies and tools while maintaining its focus on Ukraine.
Exclusive Focus on Ukraine
Since as early as 2013, Gamaredon has been targeting Ukrainian governmental institutions, with the Security Service of Ukraine linking the group to Russia’s Federal Security Service. In 2024, Gamaredon redirected all its efforts towards Ukrainian targets, aligning with its historical objective as a cyberespionage entity serving Russian interests.
Given the ongoing conflict and geopolitical tensions, Gamaredon’s relentless targeting of Ukraine is expected to persist in the foreseeable future.
Escalation of Spearphishing Campaigns
Throughout the latter half of 2024, Gamaredon’s spearphishing activities witnessed a significant surge. These campaigns, lasting anywhere from one to five days, featured emails with malicious archives or XHTML files employing HTML smuggling techniques. These files delivered malicious HTA or LNK files executing embedded VBScript downloaders like PteroSand. The graph below illustrates the increase in unique samples of these files delivered per month:
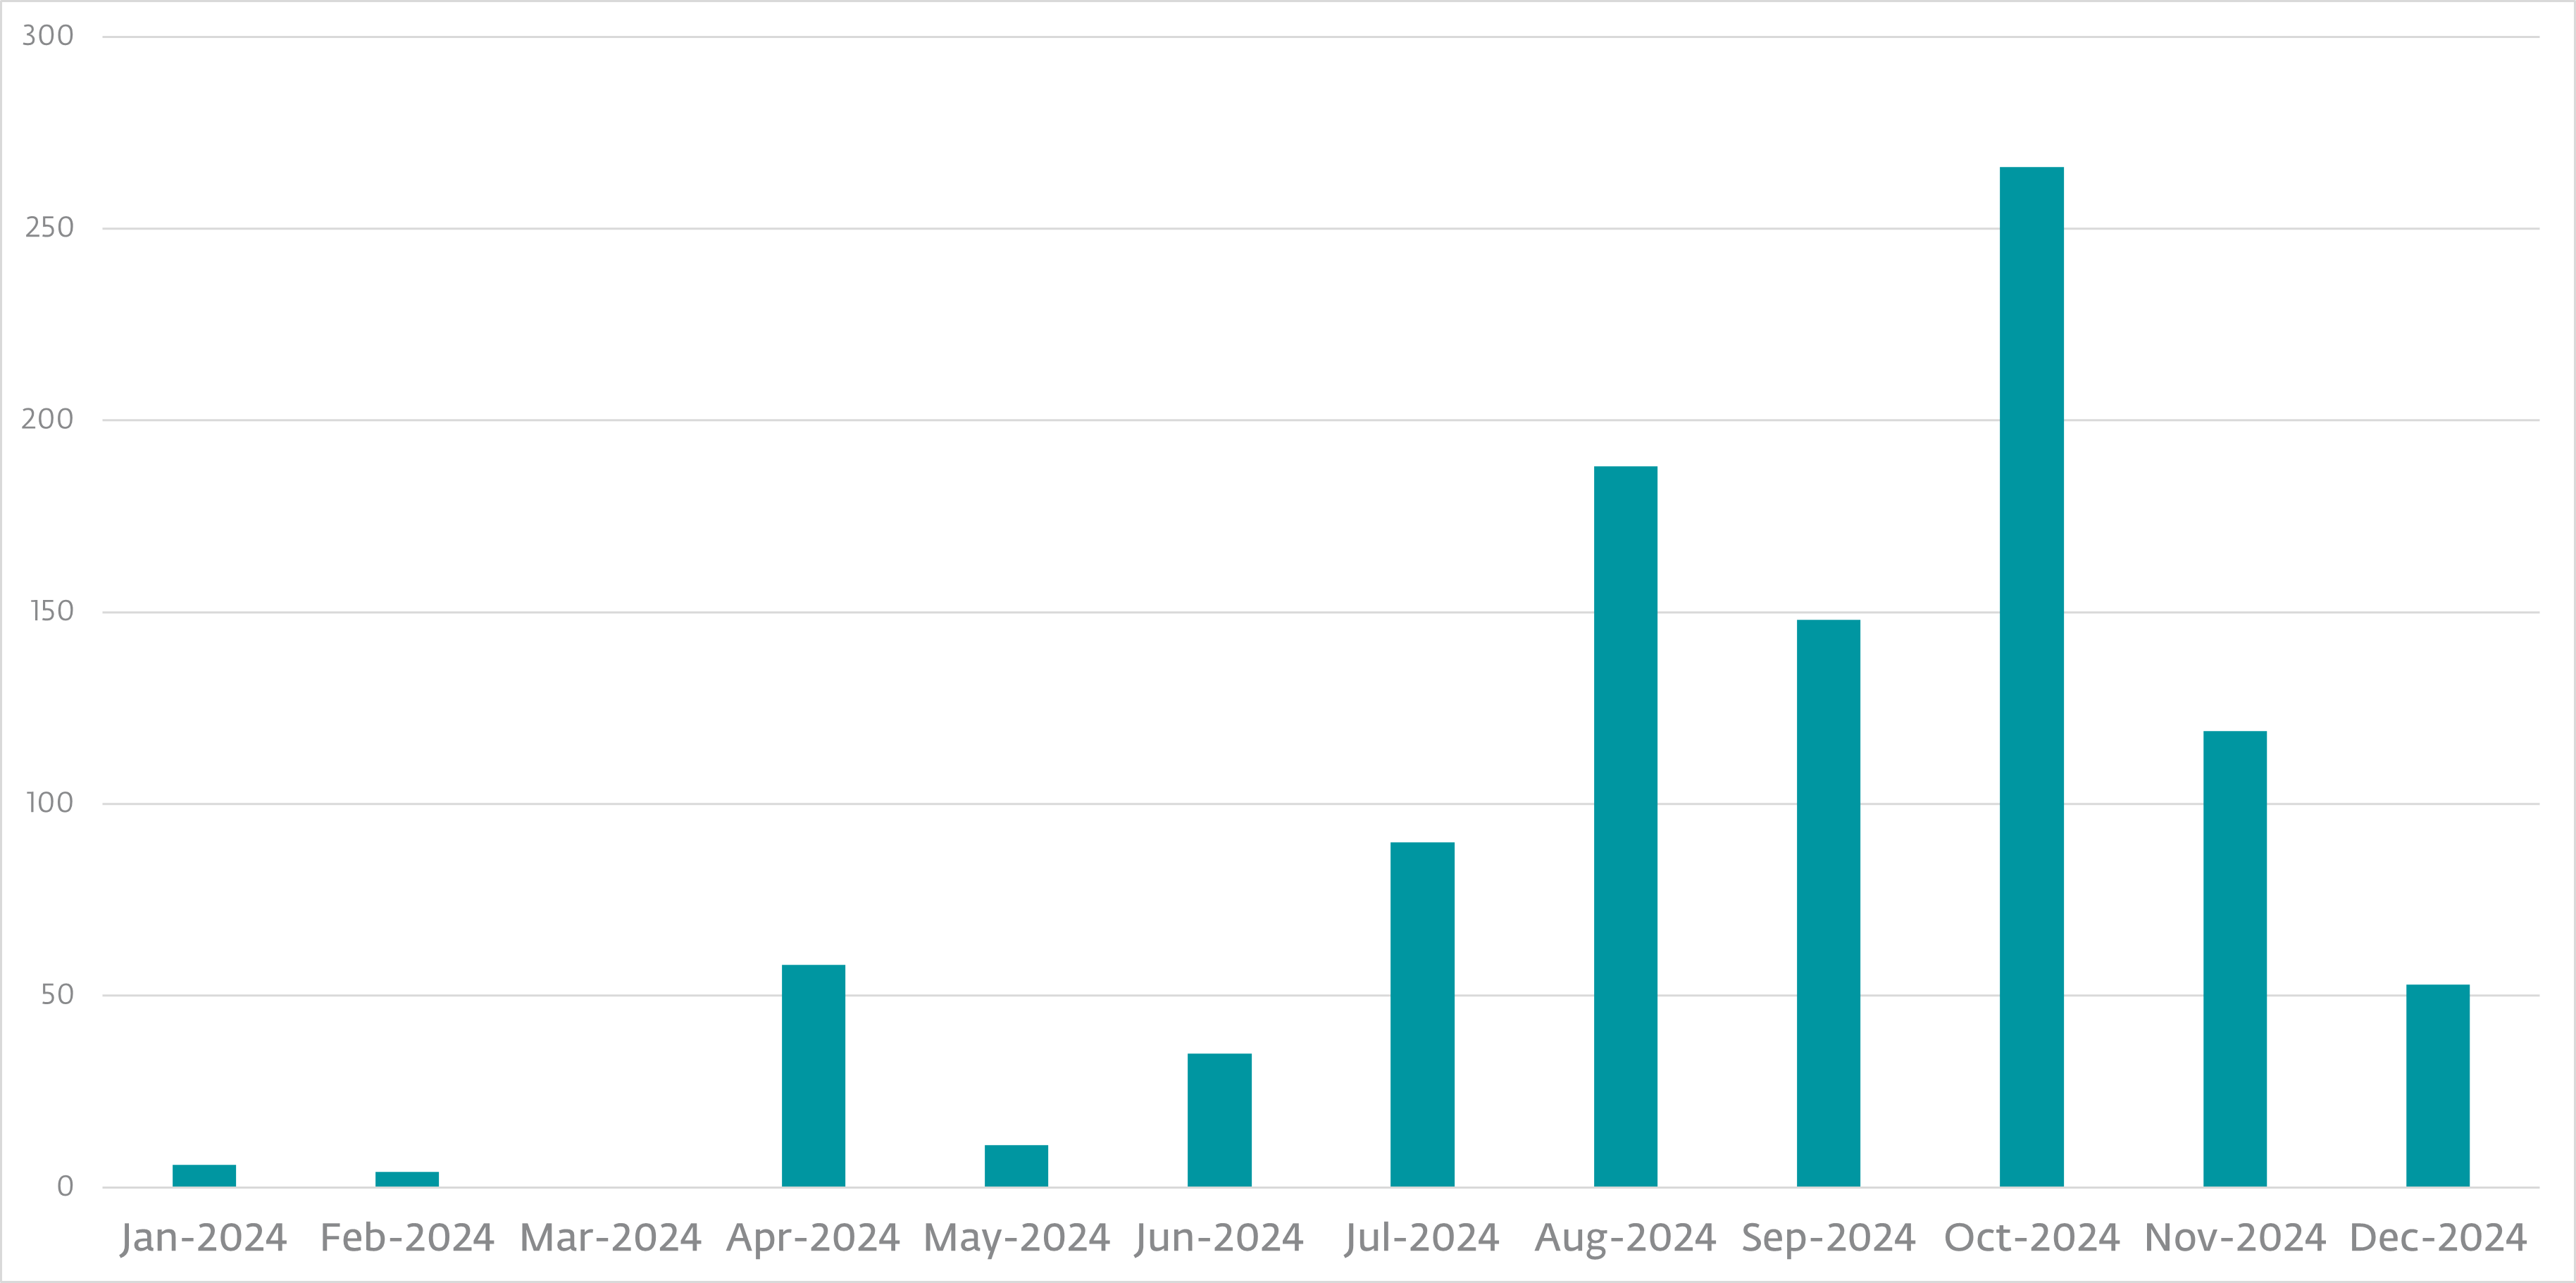
Notably, in October 2024, Gamaredon adopted a new tactic of including malicious hyperlinks in spearphishing emails, deviating from its usual attachment-based approach. Additionally, the group leveraged LNK files to run PowerShell commands from Cloudflare domains, bypassing traditional detection methods.
Toolset Evolution and Enhancements
While Gamaredon introduced fewer new tools in 2024, it dedicated resources to upgrading existing ones:
New tools unveiled in 2024:
- PteroDespair: A PowerShell reconnaissance tool for collecting diagnostic data on previously deployed malware.
- PteroTickle: A PowerShell weaponizer targeting Python applications on fixed and removable drives for lateral movement.
- PteroGraphin: A PowerShell tool using an Excel add-in persistence method for payload delivery.
- PteroStew: A VBScript downloader storing code in alternate data streams for stealth.
- PteroQuark: A VBScript downloader integrated into the PteroLNK weaponizer.
- PteroBox: A PowerShell file stealer exfiltrating data to Dropbox, emphasizing stealth and efficiency.
Updates to Existing Tools
Existing tools underwent significant upgrades in 2024:
- PteroPSDoor: Enhanced stealth techniques, including file change monitoring and registry-based code storage.
- PteroLNK (VBScript version): Improved lateral movement capabilities and obfuscation.
- PteroVDoor: Utilized new platforms like Codeberg repositories for C&C server information distribution.
- PteroPSLoad: Transitioned back to using Cloudflare tunnels for C&C infrastructure.
Unusual Payloads
In July 2024, an atypical VBScript payload was discovered, designed to open a pro-Russian Telegram channel named Guardians of Odessa. This unique payload, devoid of espionage capabilities, is attributed to Gamaredon.
Network Infrastructure and Evasion Techniques
Throughout 2024, Gamaredon persisted in evading network defenses:
- Utilized fast-flux DNS techniques to rotate IP addresses, albeit on a reduced scale.
- Depended on third-party services like Telegram, Telegraph, Codeberg, and Cloudflare tunnels for C&C infrastructure obfuscation.
- Employed DoH services and resolver websites to bypass domain-based blocking.
- Introduced new techniques like executing HTA and VBScript files from temporary directories to resolve C&C domains.
Despite operational challenges, Gamaredon remains a potent threat due to its innovation, spearphishing prowess, and persistent evasion tactics. As the conflict in Ukraine unfolds, Gamaredon will continue to adapt and intensify its cyberespionage activities.
For an in-depth technical analysis of Gamaredon’s operations in 2024 and IoCs, refer to our full white paper and GitHub repository.
For inquiries regarding our research, contact us at threatintel@eset.com.Explore ESET Research’s private APT intelligence reports and data feeds on the ESET Threat Intelligence page.