
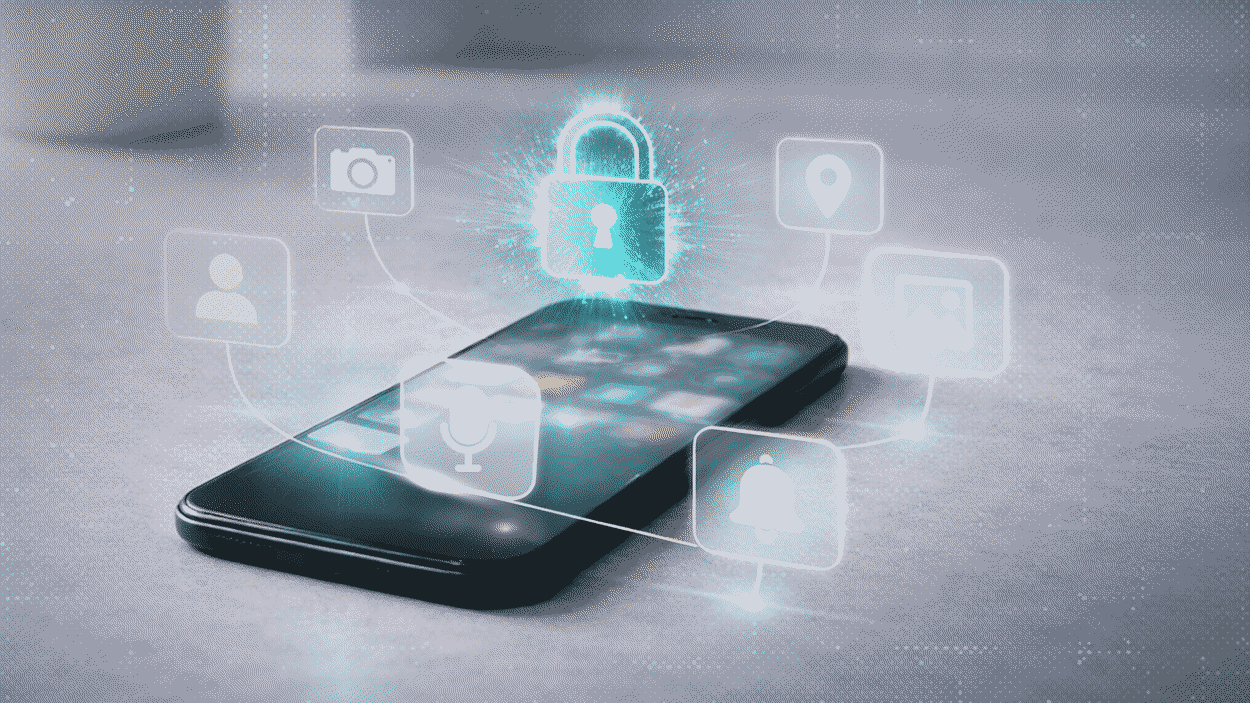
Mobile app permissions (still) matter more than you may think
Start using a new app and you’ll often be asked to grant it permissions. But blindly accepting them could expose you to serious privacy and security risks. 27 Feb 2026 […]

Start using a new app and you’ll often be asked to grant it permissions. But blindly accepting them could expose you to serious privacy and security risks. 27 Feb 2026 […]
Hey there! Did you know that AI agents now have more access and connections to enterprise systems than any other software out there? It’s true! This actually makes them a […]
Hey there, have you heard about the recent cyberattack on Anthropic’s Claude in Mexico? Attackers managed to breach multiple government agencies over a month, stealing a massive 150 GB of […]

506 Hey there, CyberNewswire readers! Exciting news from Alisa Viejo, CA! Today, One Identity has appointed Michael Henricks as their Chief Financial and Operating Officer. This strategic move showcases One […]
Anthropic Unveils Claude Code Security: A Game-Changer in Code Security Anthropic recently unveiled Claude Code Security, a groundbreaking innovation in code security that is set to revolutionize the industry. The […]

484 Hey there, readers! Let’s dive into the latest news from Wilmington, North America, where on February 24th, 2026, CyberNewswire brings you insights from a recent DMARCbis fireside chat. Are […]

Can you believe your ears? Increasingly, the answer is no. Here’s what’s at stake for your business, and how to beat the deepfakers. 23 Feb 2026 • , 4 min. […]
Anthropic Accuses Chinese AI Labs of Coordinated Distillation Attacks Anthropic made headlines by accusing three prominent Chinese AI laboratories – DeepSeek, Moonshot AI, and MiniMax – of orchestrating industrial-scale campaigns […]

Hey there, savvy shoppers and sellers! Let’s talk about the ins and outs of the social commerce platform and how to navigate it safely. It’s important to be aware of […]

For a period of four weeks commencing on January 21st, Microsoft’s Copilot had the ability to access and summarize confidential emails, despite all sensitivity labels and DLP policies specifically prohibiting […]