ESET Research has discovered a new variant of the NGate malware family that abuses a legitimate Android application called HandyPay, instead of the previously leveraged NFCGate tool. The threat actors took the app, which is used to relay NFC data, and patched it with malicious code that appears to have been AI-generated. As with previous iterations of NGate, the malicious code allows the attackers to transfer NFC data from the victim’s payment card to their own device and use it for contactless ATM cash-outs and unauthorized payments. Additionally, the code can also capture the victim’s payment card PIN and exfiltrate it to the operators’ C&C server.
Key points of this blogpost:
- ESET researchers discovered a new NGate malware variant abusing the legitimate Android HandyPay application.
- To trojanize HandyPay, threat actors most probably used GenAI, indicated by emoji left in the logs that are typical of AI-generated text.
- The campaign has been ongoing since November 2025 and targets Android users in Brazil.
- Apart from relaying NFC data, the malicious code also steals payment card PINs.
- We saw two NGate samples being distributed in the attacks: one via a fake lottery website, the other through a fake Google Play website. Both sites were hosted on the same domain, strongly implying a single threat actor.
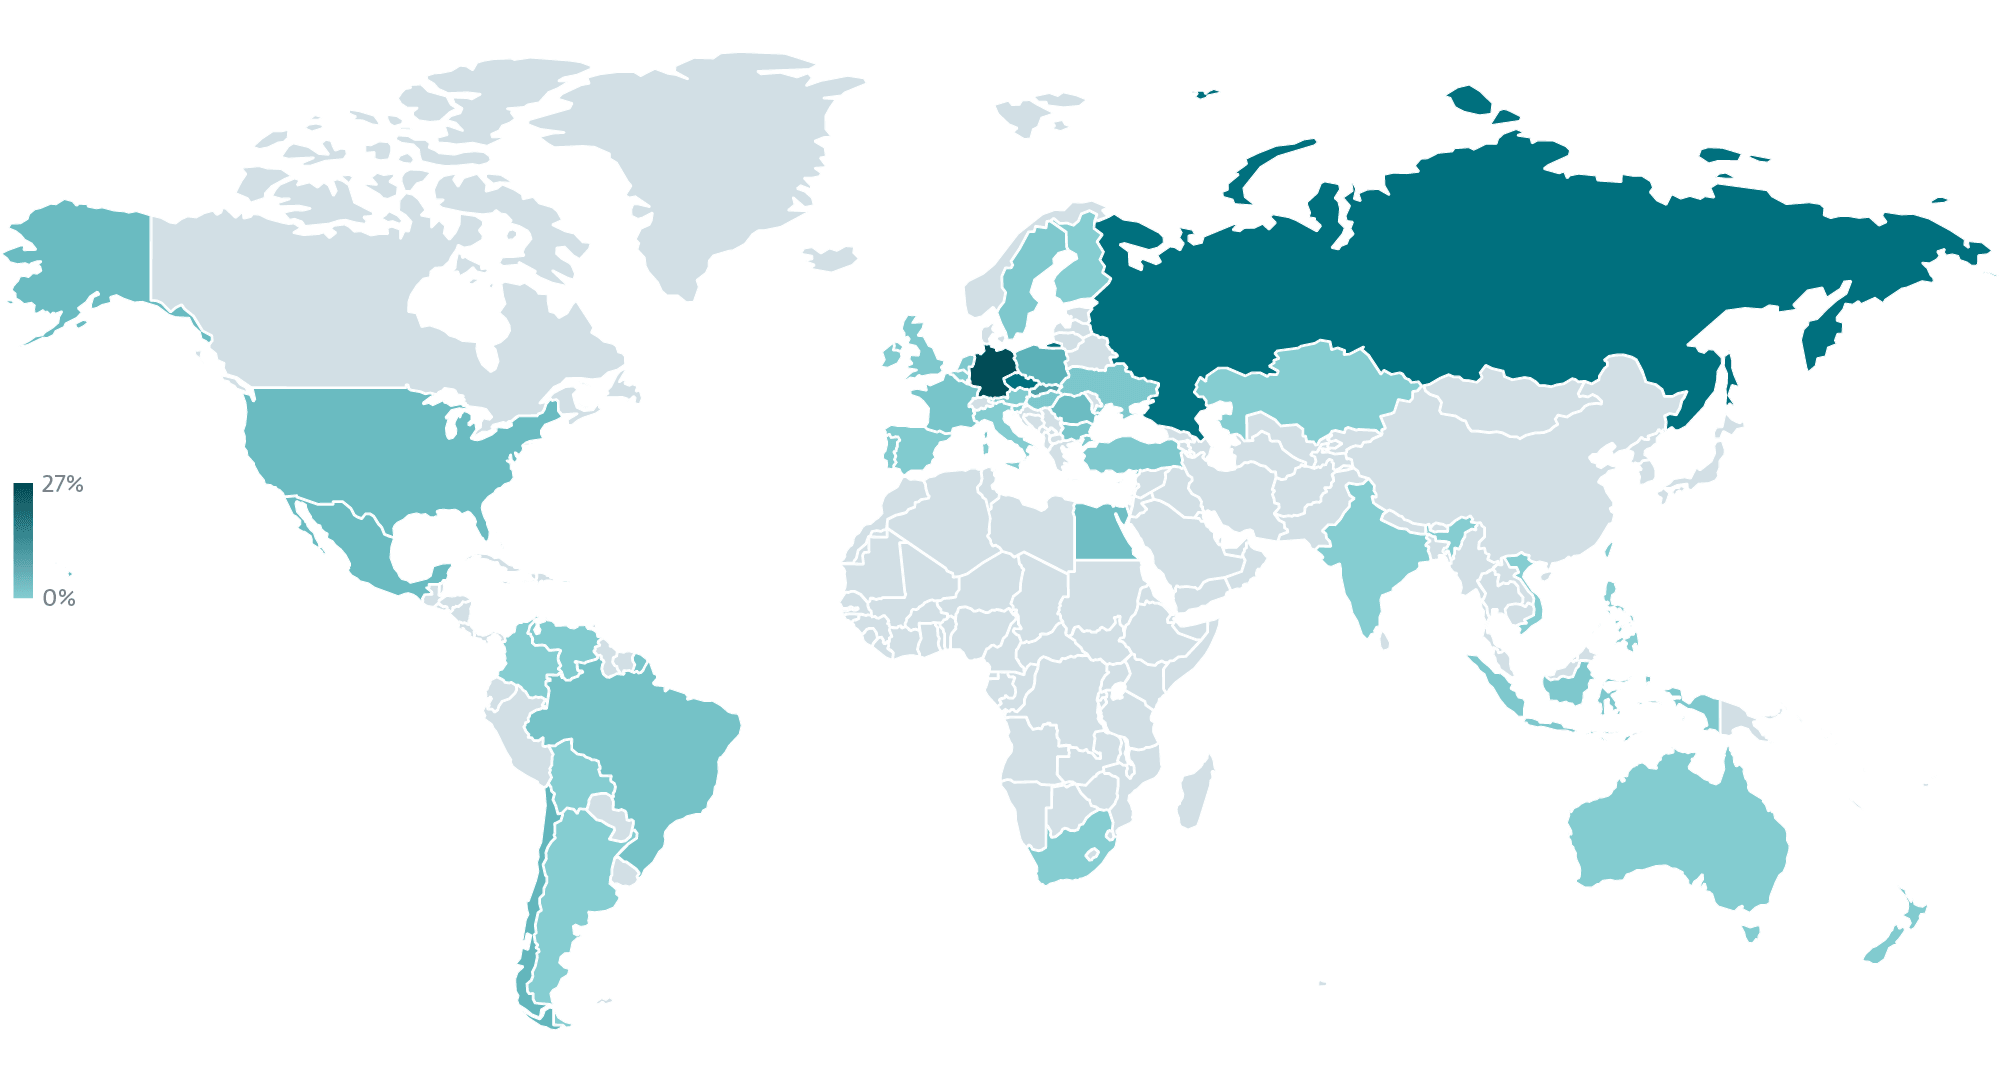
The attacks target users in Brazil, with the trojanized app being distributed mainly through a website impersonating a Brazilian lottery, Rio de Prêmios, as well as via a fake Google Play page for a supposed card protection app. This is not the first NGate campaign to take aim at Brazil: as we described in our H2 2025 Threat Report, NFC‑based attacks are expanding into new regions (see Figure 1) while leveraging more sophisticated tactics and techniques, with Brazil in particular being targeted by a variant of NGate called PhantomCard. Attackers are experimenting with fresh social engineering approaches and increasingly combining NFC abuse with banking trojan capabilities.
We believe that the campaign distributing trojanized HandyPay began around November 2025 and remains active at the time of writing this blogpost. It should also be noted that the maliciously patched version of HandyPay has never been available on the official Google Play store. As an App Defense Alliance partner, we shared our findings with Google. Android users are automatically protected against known versions of this malware by Google Play Protect, which is enabled by default on Android devices with Google Play services.
We also reached out to the HandyPay developer to alert them about the malicious use of their application. After establishing communication, they confirmed that they are conducting an internal investigation on their side.
HandyPay abuse
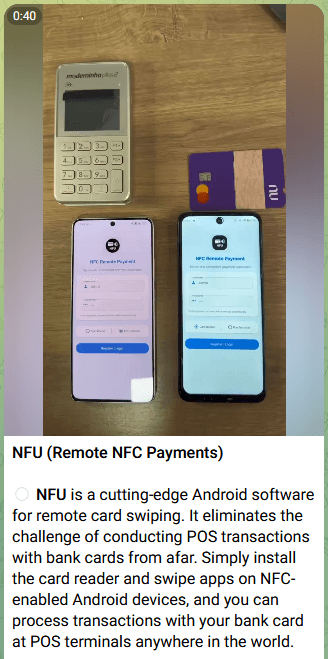
As the number of NFC threats keeps rising, so is the ecosystem supporting them becoming more robust. The first NGate attacks employed the open-source NFCGate tool to facilitate the transfer of NFC data. Since then, several malware-as-a-service (MaaS) offerings with similar functionality, such as NFU Pay and TX‑NFC, have become available for purchase. These kits are actively marketed to affiliates on Telegram (one such advertisement is depicted in Figure 2). For example, the aforementioned PhantomCard attacks that also targeted Brazil employed NFU Pay to facilitate data transfer. In the case of the campaign described in this blogpost, however, the threat actors decided to go with their own solution and maliciously patched an existing app – HandyPay.
HandyPay (official website) is an Android app that has been available on Google Play since 2021. It enables relaying NFC data from one device to another, which can be used to share a card with a family member, allow one’s child to make a one-time purchase, etc. The data is first read on the cardholder’s device and then shared with a linked device. After the users link their accounts by email, the cardholder scans their payment card via NFC, upon which the encrypted data is transferred over the internet to the paired device. That device can then execute tap-to-pay actions using the original cardholder’s card. For the process to work, the users need to set HandyPay as the default payment app and sign in with Google or an email-based token.
As per the developer’s website, the app includes a degree of monetization (see Figure 3): using the app as a reader is free (“Guest access”), but to emulate the card on a paired device (“User access”), you supposedly need to subscribe for €9.99 per month. The site, however, frames this fee as a donation and the payment is not mentioned on the official Google Play store page.
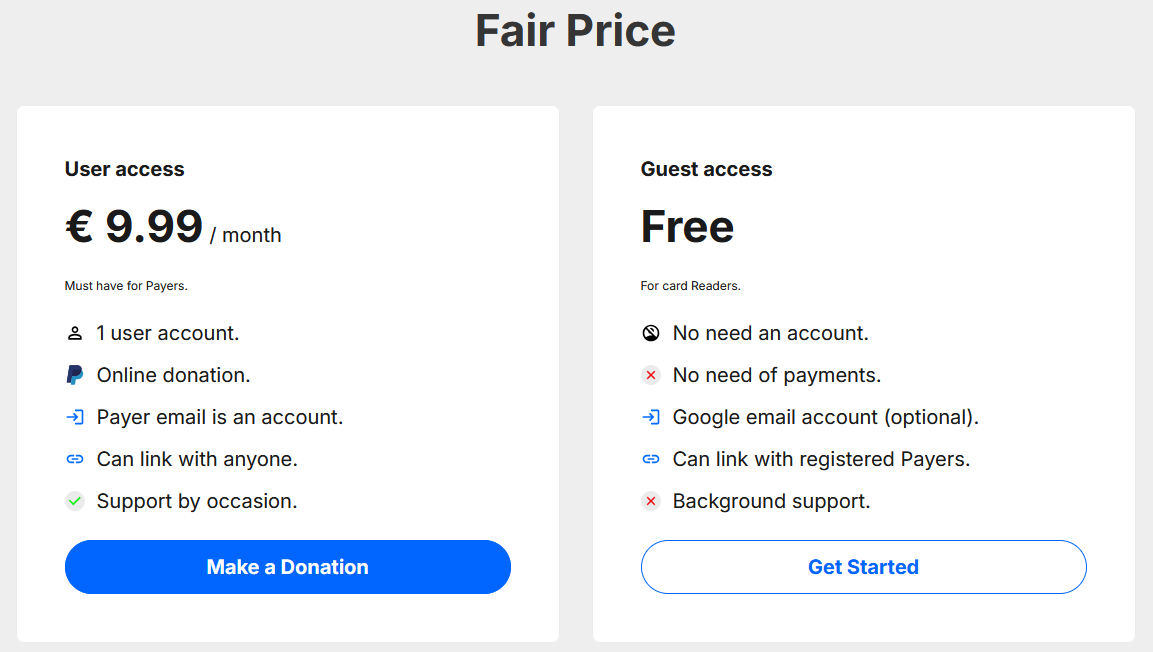
Why did the operators of this campaign decide to trojanize the HandyPay app instead of going with an established solution for relaying NFC data? The answer is simple: money. The subscription fees for existing MaaS kits run in the hundreds of dollars: NFU Pay advertises its product for almost US$400 per month, while TX-NFC goes for around US$500 per month. HandyPay, on the other hand, is significantly cheaper, only asking for the €9.99 per month donation, if even that. In addition to the price, HandyPay natively does not require any permissions, only to be made the default payment app, helping the threat actors avoid raising suspicion.
As we already alluded to in the introduction, the malicious code used to trojanize HandyPay shows signs of having been produced with the help of GenAI tools.
The malware logs show emoji commonly associated with AI-generated text, hinting that LLMs may have been used to create or alter the code, although concrete evidence is still lacking. This aligns with the broader trend of GenAI making it easier for cybercriminals, even those with limited technical expertise, to develop functional malware.
The analysis of the campaign reveals that it targets Android users in Brazil, as indicated by the distribution methods and language of the trojanized app. Logs from compromised devices in Brazil were found on the attackers’ C&C server, containing captured PIN codes, IP addresses, and timestamps related to the attacks.
The campaign involves two NGate samples distributed separately but hosted on the same domain, suggesting a coordinated effort by the same malicious actors. The first sample is disseminated through a fake website mimicking Rio de Prêmios, a lottery organization in Rio de Janeiro, while the second sample is distributed via a fake Google Play page under the name Proteção Cartão. Victims are enticed to download and install these malicious apps, compromising their devices with trojanized versions of HandyPay.
The operational flow of the trojanized HandyPay app requires manual installation outside of Google Play. The app prompts users to set it as the default payment app and then asks for their payment card PIN before relaying NFC card data to the attacker-controlled device. This allows threat actors to exploit the victim’s payment card information for unauthorized transactions. The captured data is sent to the attacker’s email address hardcoded in the malware, facilitating the misuse of the stolen information. In addition to the standard data batch transferred in the NFC relay, the victim’s payment card PIN is separately exfiltrated to a dedicated C&C server over HTTP, as shown in Figure 12. This process does not rely on HandyPay infrastructure. The C&C endpoint responsible for PIN harvesting also serves as the distribution server, consolidating both delivery and data-collection functions.
**Conclusion**
The emergence of another NGate campaign underscores the increasing prevalence of NFC fraud. This time, instead of utilizing established solutions like NFCGate or available MaaS options, threat actors opted to infect HandyPay, an application with existing NFC relay capabilities. The likely involvement of GenAI in developing the malicious code highlights how cybercriminals can exploit LLMs to cause harm without requiring advanced technical skills.
For inquiries regarding the research published on WeLiveSecurity, please reach out to us at threatintel@eset.com. ESET Research provides private APT intelligence reports and data feeds. For information about this service, visit the [ESET Threat Intelligence](https://www.eset.com/int/business/services/threat-intelligence/?utm_source=welivesecurity.com&utm_medium=referral&utm_campaign=wls-research&utm_content=new-ngate-variant-hides-in-a-trojanized-nfc-payment-app&sfdccampaignid=7011n0000017htTAAQ) page.
**IoCs**
A detailed list of indicators of compromise (IoCs) and samples can be accessed in [our GitHub repository](https://github.com/eset/malware-ioc/tree/master/ngate).
**MITRE ATT&CK Techniques**
The following table was constructed using [version 18](https://attack.mitre.org/resources/versions/) of the MITRE ATT&CK framework:
| Tactic | ID | Name | Description |
|——————-|————-|—————————–|——————————————-|
| Initial Access | T1660 | Phishing | NGate distribution through dedicated sites|
| Credential Access | T1417.002 | Input Capture: GUI Input Capture | NGate attempts to obtain PIN codes from victims |
| Exfiltration | T1646 | Exfiltration Over C2 Channel | NGate exfiltrates victims’ PINs over HTTP |
[](https://www.eset.com/int/business/services/threat-intelligence/?utm_source=welivesecurity.com&utm_medium=referral&utm_campaign=wls-research&utm_content=new-ngate-variant-hides-in-a-trojanized-nfc-payment-app&sfdccampaignid=7011n0000017htTAAQ) sentence: “The cat was sitting on the windowsill, watching the birds outside.”
Rewritten sentence: “Perched on the windowsill, the cat observed the birds in the yard.”