1.5K
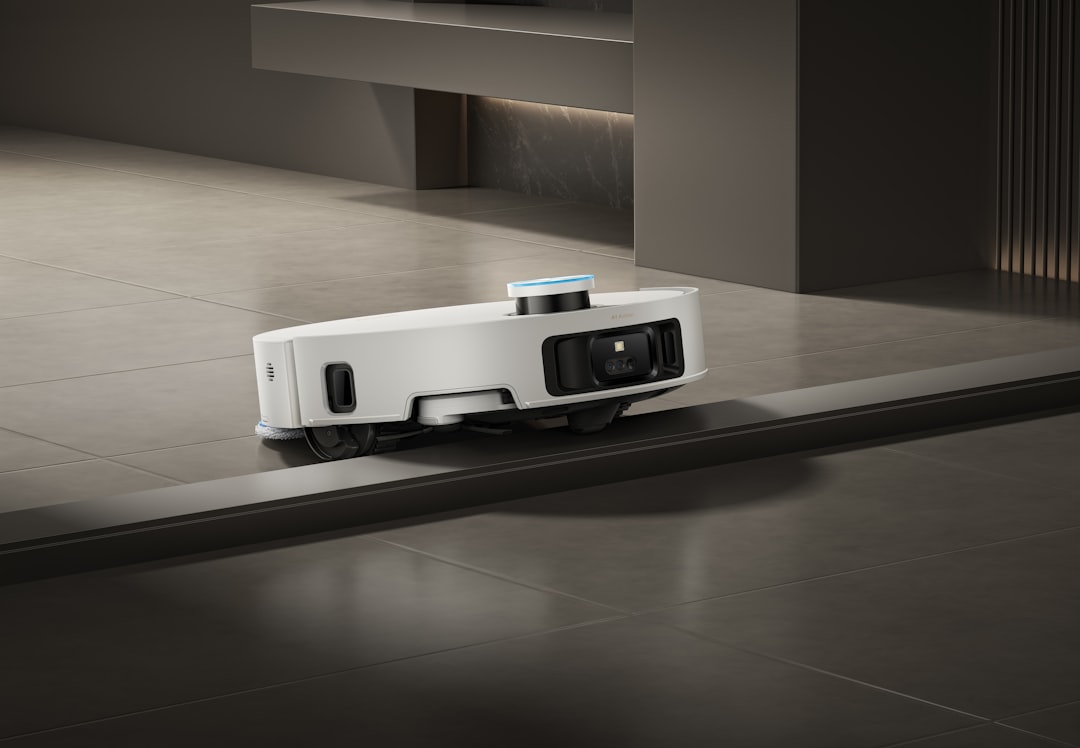
Hey there, have you heard about the latest Shark vacuum vulnerability? It’s a fascinating, yet concerning issue that allows anyone with physical access to one device to take control over other Shark robot vacuums within the same Amazon Web Services region. The flaw lies in how the AWS IoT certificates were scoped by SharkNinja, and the story behind it is quite intriguing.
Understanding the Shark vacuum vulnerability
Each Wi-Fi connected Shark vacuum comes with a unique AWS IoT certificate and a private key stored on its flash memory. The vulnerability was discovered by researcher tokay0, who found that accessing the certificate files on a Shark vacuum is surprisingly easy, requiring no authentication. This opened up a loophole where the same credentials could be used to control multiple vacuums in the region.
What’s even more alarming is that this vulnerability was not limited to a specific vacuum model but affected a range of devices. By exploiting this flaw, tokay0 was able to access sensitive information, such as live camera feeds, movement controls, home maps, and even Wi-Fi passwords stored in plain text.
The widespread impact and implications
Upon monitoring MQTT traffic in the AWS region, tokay0 discovered over 1.52 million unique device serial numbers, with a significant percentage running the vulnerable command handler. This highlighted a systemic issue rather than an isolated incident, emphasizing the importance of properly scoped AWS IoT policies to prevent such security lapses.
While the vulnerability primarily affects SharkNinja’s cloud account, it raises concerns about similar vulnerabilities in other connected products under the brand’s umbrella. The lack of a timely fix from SharkNinja further complicates the situation, leaving owners with the only option of disconnecting their vacuum from Wi-Fi to mitigate the risk.
Looking ahead and lessons learned
This incident serves as a stark reminder of the potential risks associated with shared or loosely scoped device certificates in IoT devices. The need for robust security measures and individual device scoping is crucial to prevent widespread vulnerabilities like the one seen in Shark vacuums.
While this is not the first instance of a consumer IoT fleet bug, the scale and impact of the Shark vacuum vulnerability underscore the importance of proactive security measures in connected devices. The ball is now in SharkNinja’s court to address the issue promptly and restore trust in their products.